Skip to content
Silicon Shecky

Silicon Shecky

Infosec Practitioner

  • Security is Reactionary, No Matter What Security
  • New Year, New Post, from the start General
  • First Defcon – The results Reviews
  • Defender, KQL and Lockbit Microsoft
  • Do well, not be “popular” Ramblings
  • Defense Layers: A Case Study Microsoft
  • Device vs. User Microsoft
  • Ransomware, Are You Ready? General

ALPC Bug and Carbon Black Defense

Posted on August 28, 2018August 28, 2018 By Michael Kavka 1 Comment on ALPC Bug and Carbon Black Defense

So with the drop of the ALPC 0Day (as of writing this), I decided to test the PoC on a machine running CarbonBlack Defense to see if the company I work for would be protected.

I started out with the write up from DarthSidious and followed his instructions to test.

Basically it was, open Process Explorer, download the PoC from Github, open a command prompt and Notepad. Get the PID of Notepad from Process Explorer and then watch the spool service for sub-processes (namely CMD.exe running as system).

As you can see, if you look at DarthSidious’ post it looks almost the same. There is an extra line that says “Couldn’t create remote thread 5.” This is interesting, so lets look at process explorer. In the post from DarthSidious at this point there is a cmd.exe subprocess to spoolsv.exe that is running as user NT AUTHORITY\SYSTEM. If the inject worked, that should be the same case, but when I looked at the spoolsv.exe service I saw this:

No sub-processes. Looks completely normal.

At this point I double checked that I did everything the exact way the blog post said to, and I had, so I went into the CarbonBlack Defense Console and immediately saw the following:
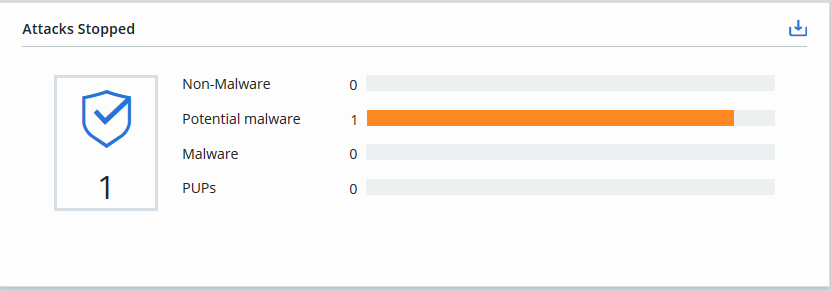
I know, it doesn’t say a lot other than an attack was stopped. Still, it is a promising thing to look at when testing. Clicking on the link into the potential malware gave me the following though:
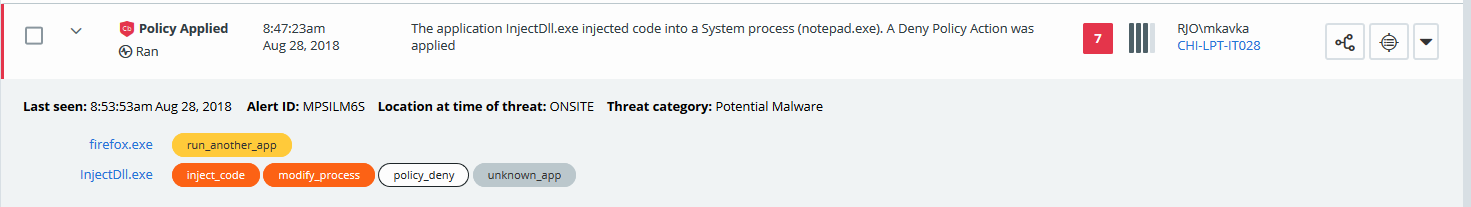
Ah Ha! it sees the PoC try to inject and hit a deny policy. So it did stop it, but lets look a little further into the information CB Defense gives us:
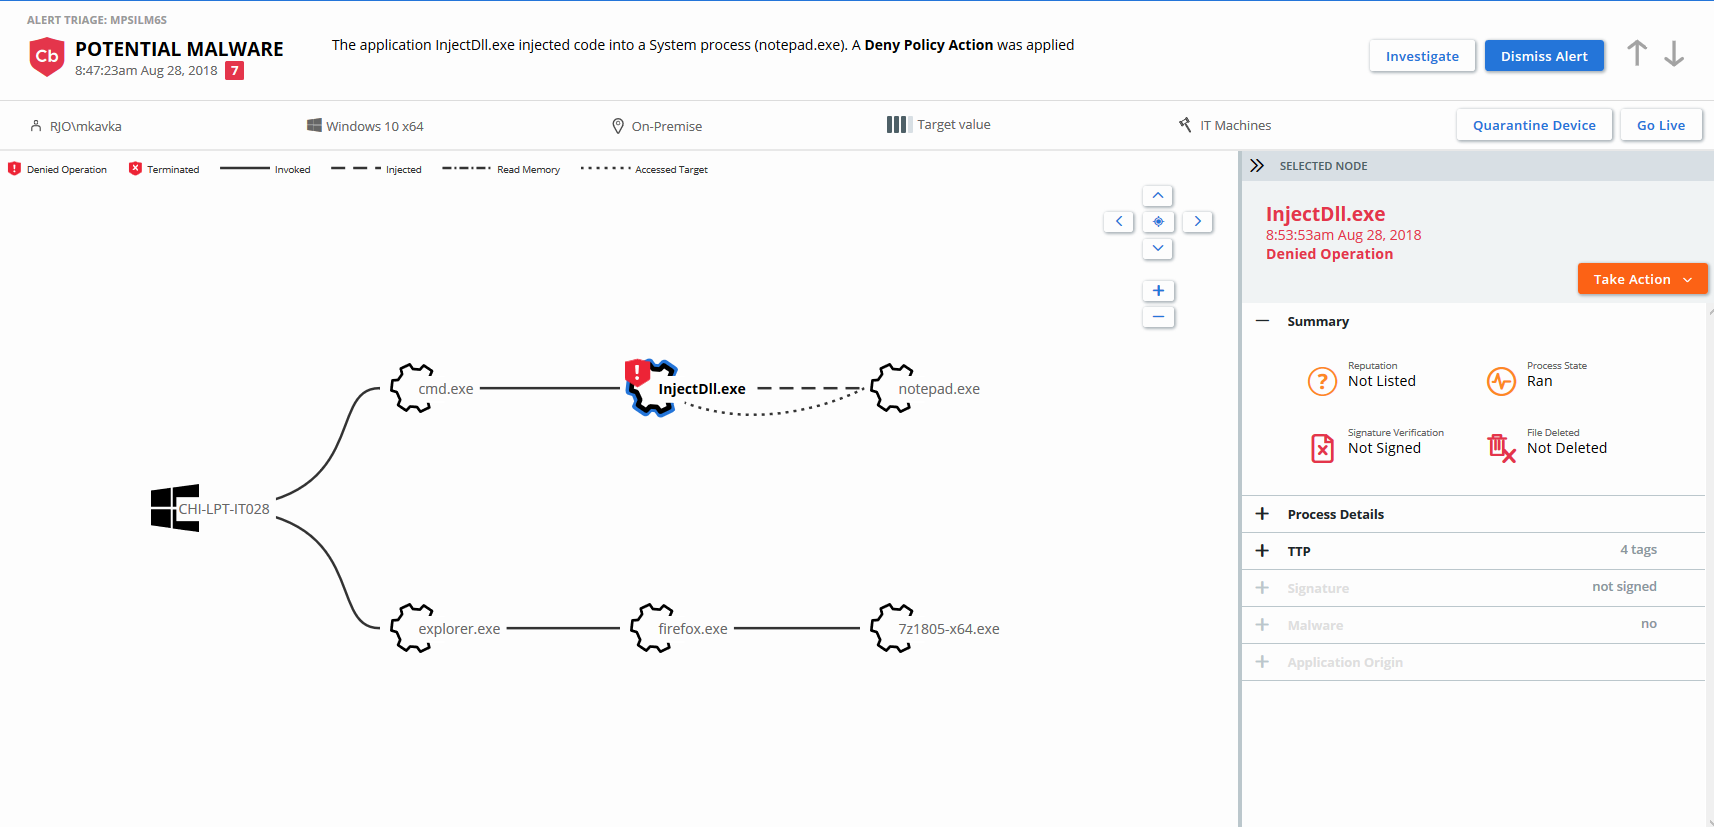
Here we can see the process layout and the injection dotted line from the PoC. The summary shows that the InjectDLL.exe is completely unknown and CarbonBlack stopped the injection process. If we go into the investigate area off the block notification we see the following:
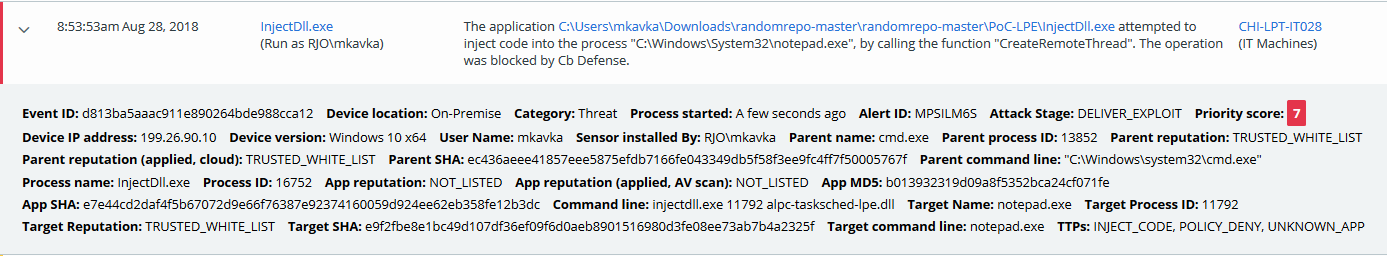
The items I found interesting from all of this is not just the TTPs, but that is saw the full command line, and shows that it was trying to deliver and exploit as the attack stage. From here I could take the hashes put them up to Virus Total, manually enter them into any protection service and pass the information onward, not that it would protect you because any chance or different file trying to use the exploit will change the hash. The bigger deal to me is that it stopped the attack with no other information than it being an unknown file and it tried to inject code.

I would hope that other EDR products would wind up stopping this attack in a similar fashion. I don’t have others to test unfortunately though. Still, with all the issues I have had with CB Defense, it is nice to see it do its job.

Security Tags:0day. Zero Day, ALPC, CarbonBlack, CB Defense

Post navigation

Previous Post: R.E.S.P.E.C.T.
Next Post: Perfect Imperfection

Related Posts

  • Security is Reactionary, No Matter What Security
  • Defender, KQL and Lockbit Microsoft
  • Defense Layers: A Case Study Microsoft
  • Device vs. User Microsoft
  • Ransomware, Are You Ready? General
  • Are you sure it is the execs? Ramblings

More Related Articles

Security is Reactionary, No Matter What Security
Defender, KQL and Lockbit Microsoft
Defense Layers: A Case Study Microsoft
Device vs. User Microsoft
Ransomware, Are You Ready? General
Are you sure it is the execs? Ramblings

Comment (1) on “ALPC Bug and Carbon Black Defense”

  1. Alexey says:
    August 28, 2018 at 10:08

    “Here we can see the process layout and the injection dotted line from the PoC. The summary shows that the InjectDLL.exe is completely unknown and CarbonBlack stopped the injection process” <— but it is nothing about 0day issue where you can change ACL of the dll via TaskJob and Hardlink… Cb can' not detect/block this.

    What CB detect and block – is old good Injection which is not 0day….

Leave a Reply

Your email address will not be published. Required fields are marked *

This site uses Akismet to reduce spam. Learn how your comment data is processed.

  • About
  • Links
    • Burbsec
    • BSides312
    • Infosec Exchange Mastodon
    • BSidesRoc
    • Hacks4Pancakes Blog
    • Krebs On Security
    • Bleeping Computer
  • Categories
    • General
    • Computers
    • Software
    • Rants
    • Security
    • Internet/Music
    • Reviews
    • Microsoft
    • Hardware
    • Mobile Computing
  • Archives
  • Social Media

Browse by tags

2008 Active Directory Android Antivirus Apple Beta CarbonBlack Chrome Computers Exchange Exchange 2007 Firefox General Thoughts Google InfoSec Internet Explorer iOS iPad IT Linux Mac Malware Microsoft OS OSx Patches SBS SBS 2008 Security Server SMB Software Support Surface TechEd Thotcon Tweets Ubuntu Verizon Virus Vista Windows Windows 7 Windows 8 XP
  • About
  • Links
    • Burbsec
    • BSides312
    • Infosec Exchange Mastodon
    • BSidesRoc
    • Hacks4Pancakes Blog
    • Krebs On Security
    • Bleeping Computer
  • Categories
    • General
    • Computers
    • Software
    • Rants
    • Security
    • Internet/Music
    • Reviews
    • Microsoft
    • Hardware
    • Mobile Computing
  • Archives
  • Social Media

Connect

  • Bluesky
  • LinkedIn
  • Mastodon
  • RSS
  • Twitter

RSS feed: iFin Intel Feed iFin Intel Feed

  • Cyberattack hits University of Munich, potentially exposing student financial data September 21, 2026
  • ShinyHunters cybercrime gang takes over Cl0p ransomware site, demands extortion payment September 21, 2026
  • Microsoft reminds admins to migrate Entra ID users to passkeys September 21, 2026 Sergiu Gatlan
  • LinkedIn wins court order blocking mass scraping of user data September 21, 2026
  • Clop gets a taste of its own medicine after ShinyHunters hijack leak site September 21, 2026
  • Google says Gemini breached three companies during security test September 21, 2026
  • Microsoft: September updates break File History backup feature September 21, 2026 Sergiu Gatlan
  • SAML: A fractal of bad design September 21, 2026
  • TerminalFix: PNG Steganography, (Mon, Sep 21st) September 21, 2026
  • Rustaceans warned of job interviews with a malicious payload September 21, 2026
  • Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO September 21, 2026 Ahmad Zaidi Said
  • From Exposure to Lockdown: How AWS Neutralizes Compromised IAM Credentials through Managed Policies September 21, 2026 Margaret Kelley

Browse by tags

2008 Active Directory Android Antivirus Apple Beta CarbonBlack Chrome Computers Exchange Exchange 2007 Firefox General Thoughts Google InfoSec Internet Explorer iOS iPad IT Linux Mac Malware Microsoft OS OSx Patches SBS SBS 2008 Security Server SMB Software Support Surface TechEd Thotcon Tweets Ubuntu Verizon Virus Vista Windows Windows 7 Windows 8 XP

RSS feed: iFin Intel Feed iFin Intel Feed

  • Cyberattack hits University of Munich, potentially exposing student financial data September 21, 2026
  • ShinyHunters cybercrime gang takes over Cl0p ransomware site, demands extortion payment September 21, 2026
  • Microsoft reminds admins to migrate Entra ID users to passkeys September 21, 2026 Sergiu Gatlan
  • LinkedIn wins court order blocking mass scraping of user data September 21, 2026
  • Clop gets a taste of its own medicine after ShinyHunters hijack leak site September 21, 2026
  • Google says Gemini breached three companies during security test September 21, 2026
  • Microsoft: September updates break File History backup feature September 21, 2026 Sergiu Gatlan
  • SAML: A fractal of bad design September 21, 2026
  • TerminalFix: PNG Steganography, (Mon, Sep 21st) September 21, 2026
  • Rustaceans warned of job interviews with a malicious payload September 21, 2026
  • Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO September 21, 2026 Ahmad Zaidi Said
  • From Exposure to Lockdown: How AWS Neutralizes Compromised IAM Credentials through Managed Policies September 21, 2026 Margaret Kelley
  • Security is Reactionary, No Matter What Security
  • New Year, New Post, from the start General
  • First Defcon – The results Reviews
  • Defender, KQL and Lockbit Microsoft
  • Do well, not be “popular” Ramblings
  • Defense Layers: A Case Study Microsoft
  • Device vs. User Microsoft
  • Ransomware, Are You Ready? General

Social Media

  • Bluesky
  • Mastodon
  • Twitter

Copyright © 2026 Silicon Shecky.